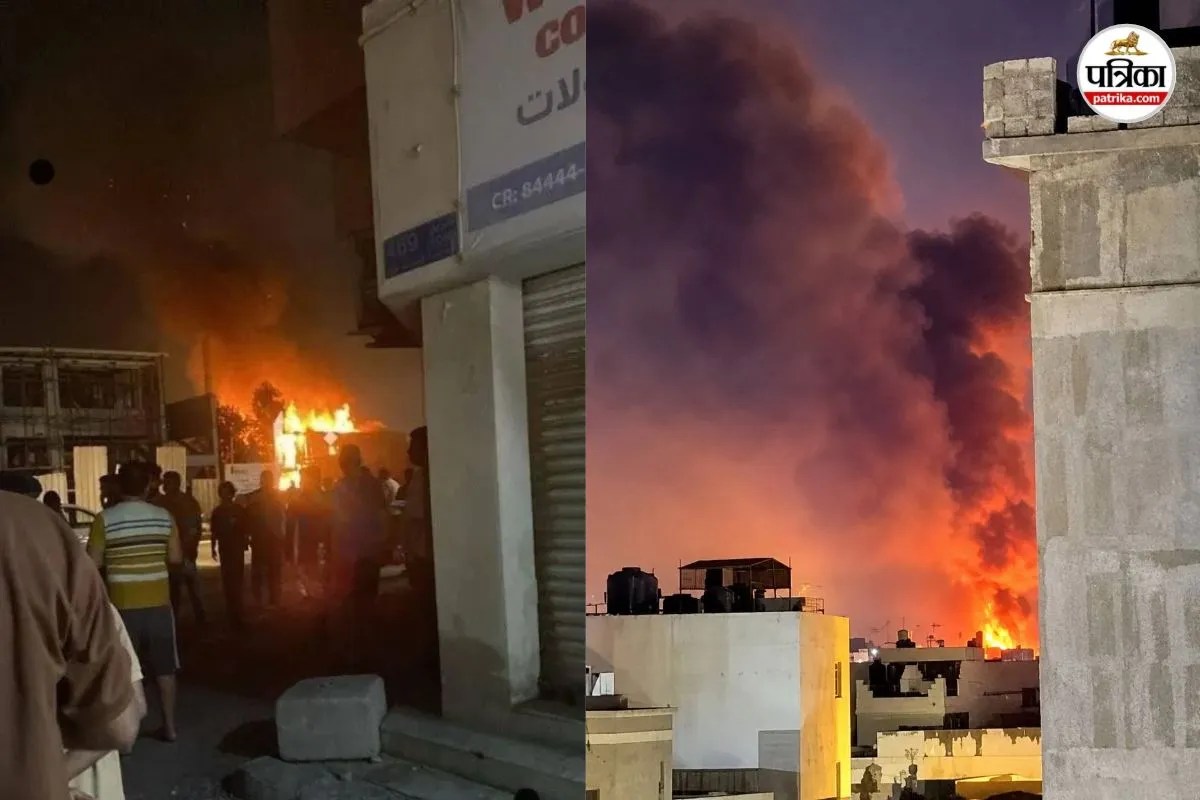
Hackers didn't just steal data last month. They turned up the heat on supermarket freezers, melted thousands of tons of food, and lit actual fires inside French grocery stores.
France has officially pointed the finger at Iran's paramilitary Revolutionary Guard, and honestly, the implications are terrifying. This wasn’t a ransomware demand or a quiet data breach. It was a direct physical assault on critical supply chains executed entirely through a computer screen.
French Foreign Minister Jean-Noël Barrot didn't mince words. Paris summoned the Iranian ambassador, called the event a major threat to national security, and vowed to push for aggressive European Union sanctions. When digital warfare starts spoiling meat and starting equipment fires in suburban aisles, the rules of global conflict have officially shifted.
The Reality of Cold Storage Vulnerabilities
Around 700 retail locations across France felt the immediate impact of the October attacks. Major chains like Intermarché, Netto, Carrefour, and Monoprix watched in real-time as refrigeration units malfunctioned, temperatures spiked, and expensive inventory spoiled overnight.
At least fifteen separate fires broke out across various stores because the hackers intentionally cranked internal temperatures past safe operational limits. Employees spent the following mornings hauling mountains of ruined groceries, melted ice cream, and spoiled meat into giant waste bins.
Cybersecurity experts shouldn't be entirely shocked by this. For years, industrial control systems and internet-connected building management tools have relied on lax security standards. Saher Naumaan, a senior threat researcher at Proofpoint, pointed out the hard truth: this attack highlights how deeply exposed everyday commercial systems are to malicious actors, rather than showcasing any kind of supreme cyber prowess from Tehran.
Beyond France: A Broader European Shockwave
The October incident wasn't an isolated French headache. Supermarkets and cold-storage distribution hubs across Belgium, Estonia, Ireland, Luxembourg, and Sweden experienced parallel temperature spikes around the exact same time.
Even the United States had a preview of this nightmare. Back in August, refrigerators in at least six American military commissaries suffered mysterious outages. Security analysts believe those incidents served as testing grounds for the wider European disruption campaign.
To make matters worse, France dodged a secondary bullet when a separate cyberattack targeted national blood banks. Hackers attempted to alter storage temperatures there too, but systems caught the anomaly before vital blood products suffered catastrophic damage.
Tracing the Invisible Footprints
Pinpointing the exact state actor behind a major cyber incident is notoriously difficult. Hackers route traffic through complex chains of packet switching across multiple countries, masking their origins. Global Cyber Risk LLC chief executive Jody Westby noted that international cooperation on cybercrime investigations remains painfully slow.
Despite those traditional hurdles, private intelligence caught up fast. Sources familiar with internal tech assessments revealed that Microsoft privately linked Iran to the cold-storage sabotage weeks before official government announcements. Now, with Paris prosecutors seeking international arrest warrants and pushing for coordinated EU economic penalties, diplomatic fallout is guaranteed.
Physical infrastructure has always been vulnerable to physical threats. What we're watching now is the terrifying normalization of remote-controlled infrastructure sabotage. Next time your local grocery store loses power or temperature control, don't automatically blame a mechanical failure. The battlefield has moved to the local refrigerator aisle, and nobody is adequately prepared.